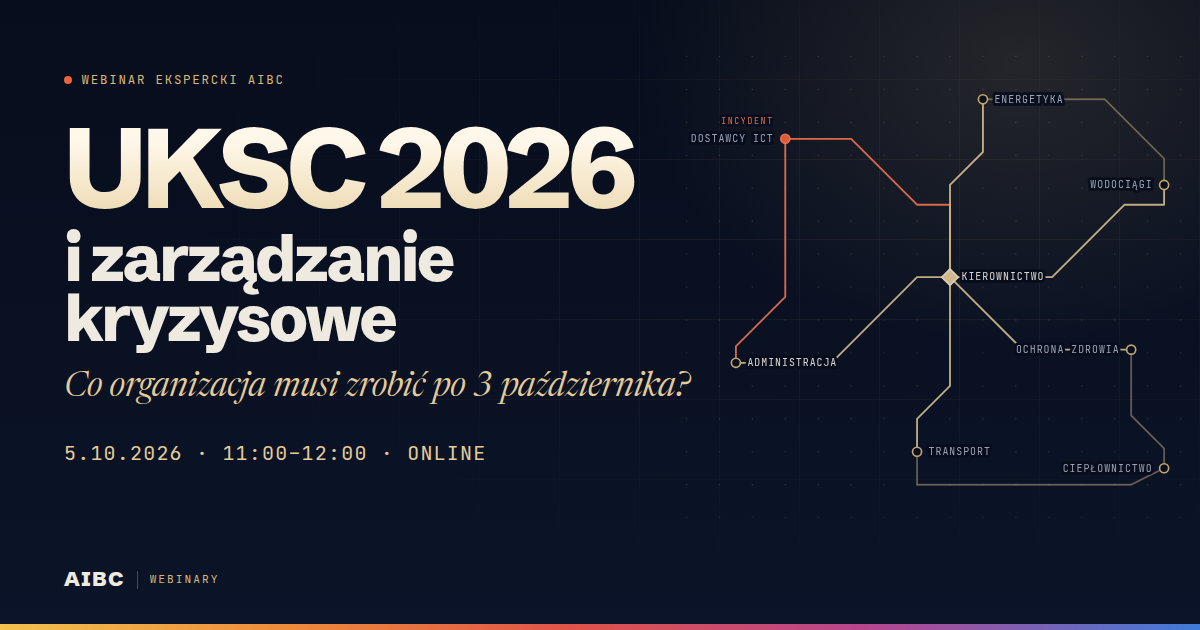
Our first AIBC webinar is a wrap: UKSC and crisis management
Two hosts, one focused hour and one clear conclusion: cybersecurity and crisis management need to meet in the same plan.
We help companies safely meet regulatory requirements and develop technology – from team training and audits, through advisory and implementation, to tailored solutions.
Regulations, client requirements and security standards translate into concrete obligations. We help you work out what your organisation needs, prepare it for an audit or certification, and implement solutions that keep working after the project ends.
NIS2 / KSCDORAMiCAGDPRISO/IEC 27001* The level and type of sanction depend on the nature of the breach and the status of the entity.
You don’t have to put it together on your own.
Our mark is made of three parts. Each stands for something we do for our clients. Together they form a whole that none of them could build alone.
We share knowledge so that teams can act, not just pass a test. NIS2 explicitly requires training for management, so we start with the board.
We connect legal requirements with the realities of your business: the audit shows how things really stand, and the advisory work turns that into an order of play. You know what applies to you and what it will cost – before you spend anything on implementation.
We build safeguards and systems that pass the audit and hold up in day-to-day work. The documentation reflects what actually works – not the other way round.
AI deployments touch personal data. Blockchain projects have a regulatory dimension. Cybersecurity is a legal requirement. That’s why we don’t split these topics into separate silos.
Audits, risk analysis and a security management system aligned with NIS2, KSC and ISO/IEC 27001.
AI deployments that save time rather than create new risks – with compliance and data-security assessment built in.
Use-case analysis, solution design and preparation for MiCA requirements.
GDPR, DORA and documentation that stands up to an auditor, because it reflects how the business really operates.
Part of our offering has a fixed scope and transparent pricing. Here you can see what each item is and who it’s for. Purchases are made on the AIBC platform.
You know where you stand on NIS2/KSC and what to tackle first.
Who it’s forcompanies that may fall under NIS2/KSC or supply entities that do
Your team spots threats in everyday work before they turn into incidents.
Who it’s forall employees, regardless of department
A set of documents and checklists for assessing your company’s readiness on your own.
Who it’s forteams that want to start at their own pace
You find out in practice how many people would click a suspicious link.
Who it’s fororganisations with up to 50 users
Secure deployment and use of AI tools in your organisation.
Who it’s forcompanies deploying or planning to deploy AI
Clear rules for working with AI tools, without data leaks.
Who it’s forteams that use AI tools every day
We identify which regulations and risks actually apply to you. The outcome is a short report with priorities, not a pile of documents.
We set out the order of actions, the budget and responsibilities. You know what to do in the first quarter and what can wait.
We put safeguards, procedures and tools in place together with your team, training the people who will work with them along the way.
Reviews, updates after legal changes and audit support. Compliance stays in place a year on, too.
Four questions and you get an initial overview straight away. No personal data required.
News about the company, events, regulatory changes and the technologies we work with.
View all →
AIBC has achieved ISO/IEC 27001:2023 certification. We went through the same journey we help clients navigate – from building the system to an independent audit.
Two hosts, one focused hour and one clear conclusion: cybersecurity and crisis management need to meet in the same plan.
This time we went to the energy security conference without slides, but with an open notebook. Cyber-physical resilience stayed with us most.
Tell us what you’re facing. We’ll come back with a proposal for the next step.
We usually reply within one business day.